Recruitment data.
Clear responsibilities.
Verified controls.
Tenant-bound access, role permissions, private document workflows, audit history and guarded service connections protect the operational records your agency relies on.
Rimo is operated by Axamy Group Limited, company number 17438182.
- 01Authenticated accountEstablish the staff identity
- 02Active tenant membershipVerify company scope and lifecycle
- 03Role & module permissionCheck the requested action
Protected data · Private documents · Audit history
This page describes controls implemented in the current Rimo codebase and operational design. It does not claim ISO 27001, SOC 2, Cyber Essentials, a specific data-centre region, an uptime guarantee or a backup frequency that has not been separately evidenced.
Authority follows the company and the action.
Access is not based only on knowing a workspace URL. Identity, active membership, tenant scope, lifecycle status and module permission are used to guard data and workflow operations.
- 01Authenticated workspace access
- Staff access is tied to an authenticated account and active tenant membership.
- 02Tenant separation
- Canonical records are tenant-bound and database row-level security is enforced for protected data.
- 03Role and module permissions
- Consultant, manager, compliance, finance and administration access can be scoped to the modules needed for the role.
- 04Lifecycle controls
- Trial, paid, suspended and offboarding states are checked before protected mutations and automation.
- 05Server-owned authority
- Sensitive operations use guarded server or database functions rather than trusting browser-supplied tenant identity.
- 06Conflict protection
- Version and compare-and-set controls protect supported records from silent concurrent overwrites.
Evidence follows a controlled lifecycle.
Candidate and staff document workflows bind uploads to the tenant, candidate and document record. File size, declared type and inspected bytes are validated before evidence becomes available.
- Private object paths and bounded upload size
- File-type and byte inspection
- Checksum verification where exposed
- Malware scan queue
- Quarantine until validated
- Expired-upload cleanup and exact-path deletion
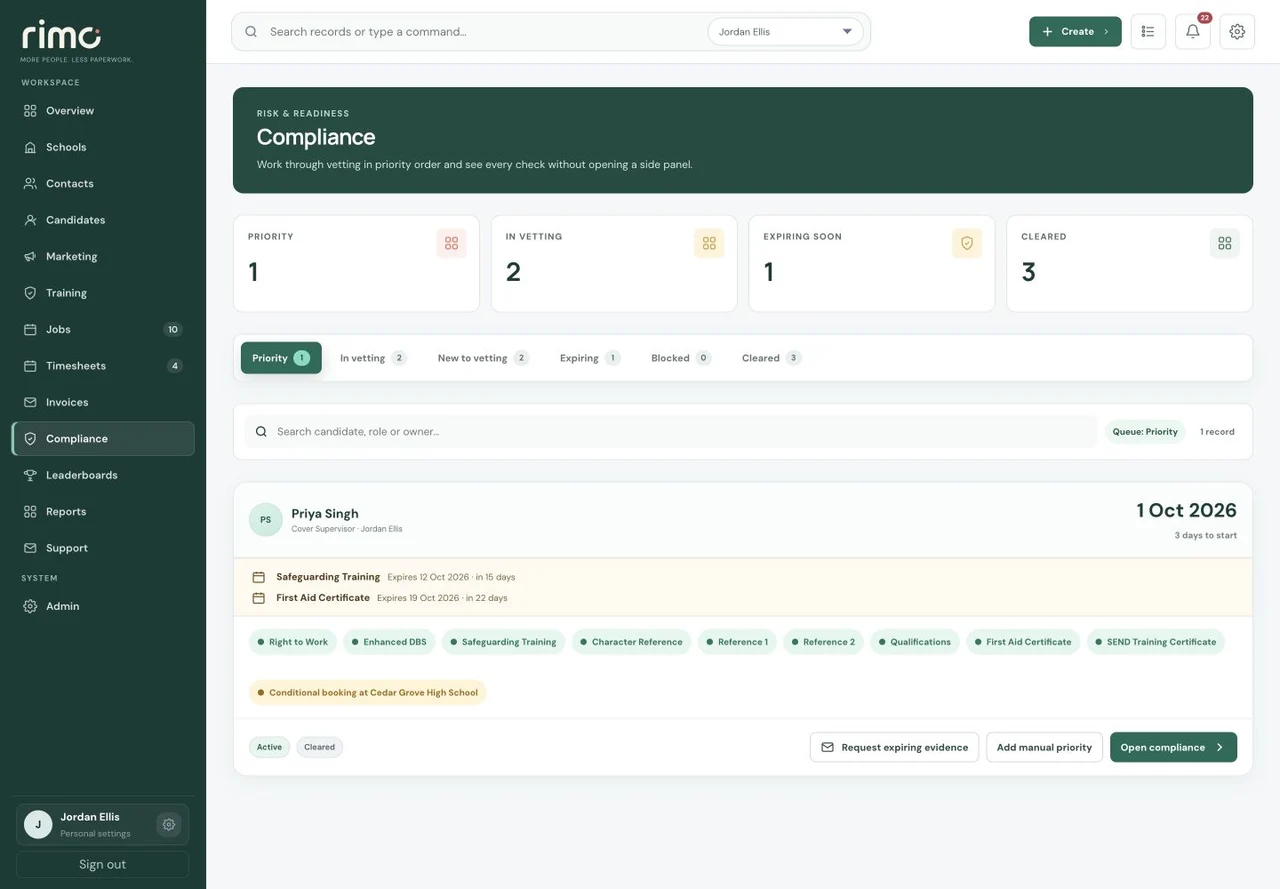
Product view · fictional demonstration data
- UploadPrivate, tenant-bound path
- ValidateSize, type and file inspection
- ScanQuarantine until validated
- Make availableControlled document access
Important actions leave operational evidence.
Rimo maintains tenant-scoped records for supported audit, email-delivery, public-form and document workflows, with bounded service operations and idempotency protection where duplicate delivery would be risky.
- 01Audit history
- Supported record changes and workflow events are written to tenant-scoped audit history for later review.
- 02Delivery ledgers
- Automated and system email paths use durable identity and delivery records to reduce unsafe duplicate sends.
- 03Exports and offboarding
- Company export and offboarding workflows are permission-gated and designed around exact tenant scope.
Customer recruitment mail.
Separate system notifications.
Supported customer messages use the verified Microsoft organisation connection and authorised mailbox routing configured for that workspace. Rimo technical and system notifications use a separate controlled pipeline.
- Organisation-level Microsoft connection
- Authorised users and shared mailboxes
- Tenant-bound mailbox selection
- Verified purpose routing
- Durable delivery identity
- Separate system notifications
Recovery and visibility matter too.
The repository includes database and storage backup tooling, restoration workflows, technical monitoring and production-readiness checks.
Current customer due diligence should request the latest evidence for the production environment rather than relying on a static marketing promise.
- 01Backup tooling
- Database and private-storage backup jobs are maintained separately from the live application workflow.
- 02Restore process
- Restoration tooling and drill procedures support validating that protected backup outputs can be used.
- 03Technical monitoring
- Health endpoints and technical monitoring cover core service availability and worker status.
- 04Environment isolation
- Production and staging configuration are checked to prevent unproved cross-environment data access.
- 05Security headers
- The public deployment defines transport, content, framing, referrer and browser-permission controls.
- 06Release gates
- Automated tests and production-readiness scripts check migrations, configuration and guarded workflows before cutover.
Ask for evidence.
Not badges.
Discuss the product and the current production environment as part of your due diligence.
Does Rimo claim ISO 27001, SOC 2 or Cyber Essentials?
No certification claim is made on this page. If a certification becomes available, it should be supported by current evidence and scope.
Are company workspaces separated?
Yes. Protected canonical data is tenant-bound, database row-level security is enforced and sensitive service operations verify tenant membership and permission.
How are uploaded documents handled?
Supported direct-upload workflows use private tenant-bound paths, bounded files, server-side validation and malware scanning before final availability.
Can customers export their data?
Rimo includes an authorised company export workflow. The exact export coverage and offboarding assistance should be confirmed against the current implementation and customer agreement.
Where is the data hosted and how often is it backed up?
Those answers depend on the current contracted production environment and operational schedule. Request the latest deployment and backup evidence during due diligence rather than relying on an unverified general statement.
Review the controls.
Bring your security requirements and due-diligence questions.